A Kickstarting Workshop
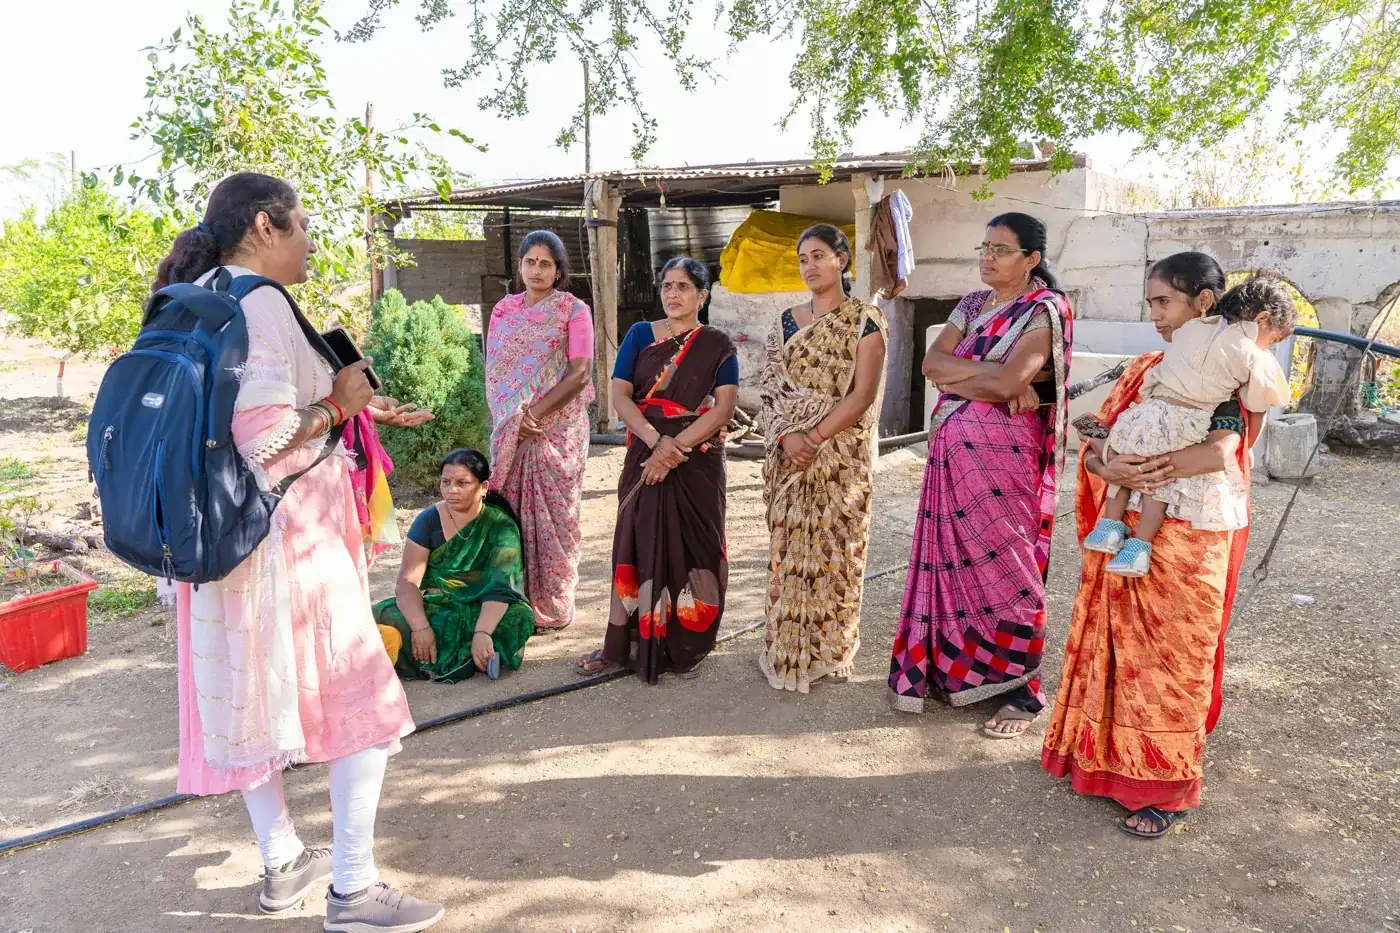
A working session with your leadership and team leads to agree scope, owners and the first 90 days.
Your all-in-one DPDP compliance partner & platform.
We take the whole journey with you. We work out where you stand, bring your teams along, connect a consent platform to every system you run, and work on the ground with your programmes until the job is done.
DPDP implementations delivered, from the first baseline to compliance that runs day to day.
Implementationssystems integrated, so consent and data requests reach every place the data lives.
System integrationstraining workshops run, so the people who handle data know what to do and why.
Training workshopsconsents captured and on record, each one ready to show when it is asked for.
Consents capturedOur promise
Most organisations buy one piece of DPDP help. An awareness session, a legal opinion or a software license. Each is useful, and each leaves you to do the hard part alone. With Commons you get all of it, run as one program with one team.
| What it takes to be compliant | Commons Trust | Awareness session | Legal consultation | Consent software |
|---|---|---|---|---|
| Understand what the law asks of you | Yes | Yes | Yes | Some |
| Find what personal data you hold, and where it sits | Yes | No | Some | No |
| Write your policies and notices | Yes | No | Yes | Templates |
| Train every team and change how they work | Yes | One talk | No | No |
| Consent connected to all your systems | We integrate | No | No | You integrate |
| Clean old data and ask old users for consent | Yes | No | No | No |
| Stay until you are compliant | Yes | No | No | No |
Scroll sideways to see every column.
What you get
Whichever stage you start from, these come as standard. Nothing to assemble, and nothing sold as an add-on later.
A working session with your leadership and team leads to agree scope, owners and the first 90 days.
67 questions answered by your teams, and every gap ranked by the penalty it carries.
Every app, sheet, form and vendor that holds personal data, and why you keep it.
Board-ready policies, and every control tied to the section of the Act or Rules it comes from.
A named owner, a champion in every team, and a dated plan everyone can see.
Every purpose, notice and consent record in one place, with the full history of each choice.
Connectors, an API and an SDK, wired into your CRM, survey tools, HR and your own apps.
Where the people you serve see what you hold, change their choices and make requests.
Role-wise sessions in the languages your teams speak, with every sign-off tracked.
Campaigns that reach old and new users on WhatsApp, SMS, calls and field visits, in their language.
Vendors, partners and grantees who handle your data, with contracts, renewals and alerts in one place.
A page you share with funders, donors and customers that shows how you handle their data.
Your compliance journey with Commons
The four stretches overlap. Your field teams can be cleaning old records while engineers connect your systems, and the policies land before the first training session.
We get stakeholders on the same page & align to a goal.
Baseline done by 9 people. Biggest gaps: breach response, vendors, children's consent.
Policies, notices and processes built around how each of your teams actually works.
Our engineers connect it to every system you run, standard or custom.
We train every team, then embed in your programmes and projects until the work is done.
We don't leave until you're compliant. You keep an evidence pack that shows the Board, your auditors and your funders exactly how.
Plan your journey with usHow long it takes
Pick your organisation's size and how fast you want to move.
The Commons Trust platform
Consent is a promise you make to a person. Commons Trust is where you keep it: one record of what each person agrees to, in the language they understand.
For your privacy teamA command centre that shows what's due, what's at risk and what the evidence says.
For the people you serveNotices they can read or hear in their own language, and a one-tap way to change their mind.
For your engineersAn API, an SDK and connectors, so consent travels with the data instead of sitting in a PDF.
आपकी जानकारी, आपकी मर्ज़ी
हम आपके बच्चे का नाम, फ़ोन नंबर और गाँव रखते हैं ताकि ट्यूशन चला सकें। बाकी हर काम के लिए आप चुनें।
कभी भी WhatsApp पर “वापस” लिखें
One screen for the whole programme: how ready you are, what's due, and what to do next. Readiness only counts a control as done when the evidence is on file.
Example organisation and figuresGood morning, Meera
Aarambh Foundation · 6 programmes · 3 states
Evidence-backed readiness
96 of 129 controls done, weighted by penalty.
Up from 22% in March
Until the obligations commence
13 May 2027 · on track
Consent by channel
This monthKey actions
3 of 33VND-02Send updated processing terms to 4 vendorsWorth ₹250 crore if it goes wrongDue FriREQ-118Donor erasure, waiting on paymentsRaised on WhatsApp · identity checked3 daysSYS-07Kobo server stopped syncing consentLast checked 2 hours agoFixEach team answers the questions about its own work. Anything nobody can answer shows up as a gap, and every answer explains which part of the law it comes from.
Example organisation and figuresBaseline assessment
Round 2 · 52 of 67 answered
Answered by Priya S., Programmes. The tutoring and scholarship programmes enrol children, so you need a parent's verifiable consent before using their data (Act, Section 9).
Readiness by area
Weighted by penaltyEvery reason you hold people's data, written the way the public will read it. Notices are built from this register, so what people agree to always matches what your systems do.
Example organisation and figuresPurposes
14 on the register · notice v3 · updated 2 Oct
Requests arrive on WhatsApp, the helpline, the website or through a field worker. They land in one queue with a clock on each, and an erasure reaches every connected system.
Example organisation and figuresRights requests
12 open · median reply 6 days · none overdue
| Request | Channel | Status | Due |
|---|---|---|---|
| Erase my dataR. K••••• · donor | In progress | 3 days | |
| What do you hold on me?S. M••••• · volunteer | Website | Identity checked | 11 days |
| Correct my child's nameA. P••••• · parent | Field app | Done | Closed |
| Complaint about callsV. D••••• · beneficiary | Helpline | With grievance officer | 24 days |
| Name a nomineeK. B••••• · beneficiary | Field app | New | 41 days |
REQ-118 · Erase my data
4 of 5Found in 5 systems
Every control the Act and Rules ask of you, each tied to the section it comes from. A control only counts as done when its evidence is in the vault.
Example organisation and figuresControls
129 in scope · 10 out of scope, with reasons
96 done · 21 started · 12 not started
Backed by evidence| Control | From | Evidence | Status |
|---|---|---|---|
| SEC-05 · Keep logs for at least a yearOwner: IT lead | Rule 6 | log-policy.pdfsiem.png | Done |
| CHD-01 · Work out whether you hold children's dataOwner: Programmes | Section 9 | data-map.xlsxbaseline Q3 | Done |
| VND-02 · Contracts carry the security obligationsOwner: Legal and finance | Section 8 | 7 of 11 signed | Started |
| BRC-01 · Run a breach drill this yearOwner: Data protection lead | Rule 7 | drill booked 14 Nov | Started |
| RET-03 · Tell people before you erase their dataOwner: Programmes | Rule 8 | None yet | Not started |
Accountability
Ownership
Someone has to answer for DPDP, all the way up to the board or the trustees. Large organisations notified as Significant Data Fiduciaries must appoint a Data Protection Officer based in India who reports to the board.
Rights
People can ask to see, correct or erase their data, complain, or name someone to act for them. Done by hand, one erasure across a CRM, a survey tool and a payments system can take weeks of staff time.
Evidence
When the Board, an auditor or a funder asks, leadership needs proof already on hand. In a good programme the evidence builds up as a by-product of everyday work.
Breaches
When data leaks, the Rules expect you to tell the people affected and the Board without delay, and to send the Board a detailed report within 72 hours. That only works if everyone already knows their part.
Who it's for
The law is the same for everyone, but the hard part is different for each kind of organisation. We start where the risk is.
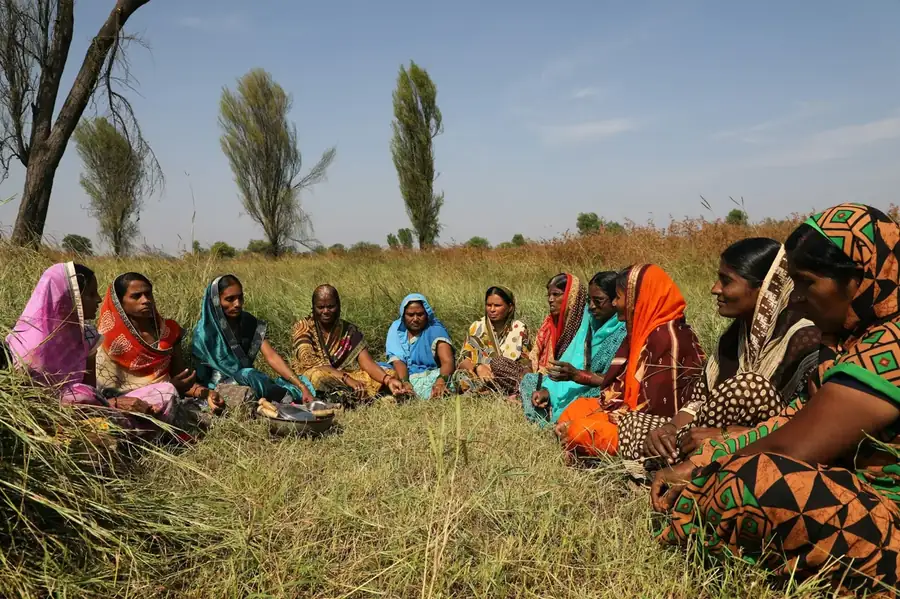
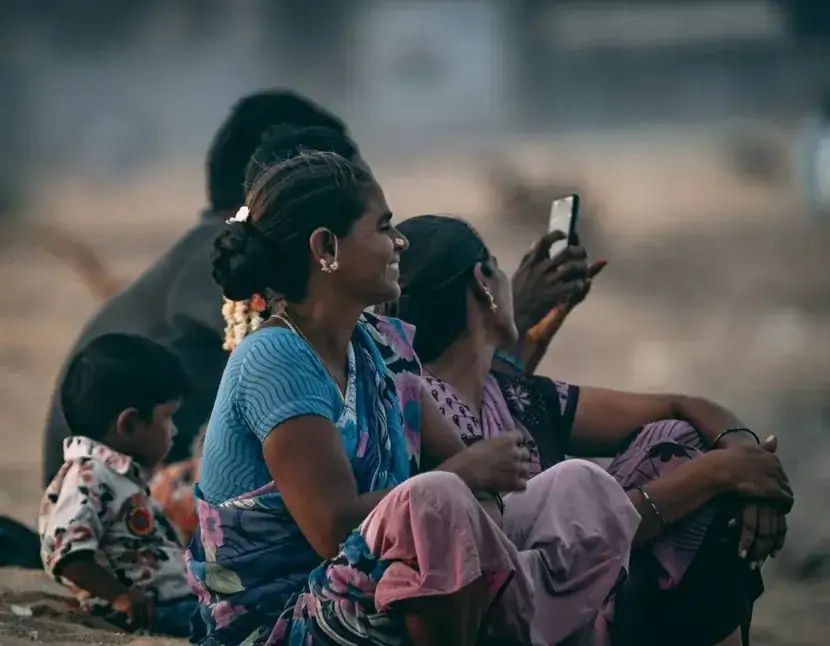
Children, health records and years of paper forms. Field teams who collect data offline in villages, and very little IT staff.
Grantee data flowing in from dozens of partners, scholarship applicants, and a board that wants assurance across the portfolio.
Fast-moving product teams, analytics everywhere, and investors or enterprise customers asking about DPDP in due diligence.
Customers, employees, vendors and many systems across business units, often with a Significant Data Fiduciary label coming.
Unbundled Services
Some teams already have a lawyer, or already have a consent tool. Take the part you're missing.
Know exactly where you stand and what to fix first. Try the free self-assessment.
Everything written down, approved, and ready to run.
Use it yourself, or have our engineers connect your systems.
A team that trains your people and sorts old data in the field.
Take the whole journey and one team is answerable for the result, from the first baseline question to the last record cleaned up in the field.
Talk about the journeyThe countdown
The work runs in a fixed order. First you find the data, then you send fresh notices, then consent and rights have to work in every system. Each step takes weeks, so a late start squeezes everything after it.
The DPDP Act is passed by Parliament.
The DPDP Rules are notified and the Data Protection Board is set up.
Consent Manager rules apply. Registered Consent Managers can start operating.
Notices, consent, security, breach reporting, children's data and rights all apply, with penalties.
Working back from 13 May 2027, a mid-sized organisation needs to start its baseline now to finish on time. See the month-by-month plan.
Plan back from the deadlineStart here
Take the two-minute check for a rough picture, then send us your details. We'll reply within two working days. Want the full picture? Take the readiness baseline, section by section.
Case studies
What the work looked like, what was hard, and the numbers at the end. Clients are not named; the facts are theirs.
Guides
Plain-language guides to the Act and the Rules, written from inside real compliance programmes. Free to read, share and quote.
Questions
Have a question that isn't here? , or write to hello@commons.inc.
Mostly operations. The Act is short and readable; its obligations land on intake forms, field apps, CRMs, vendor contracts and the habits of hundreds of people. Legal advice tells you what the law means. It doesn't change how a field worker enrols a family on a Tuesday afternoon.
That is why we put strategy, design, systems and on-ground work in one programme. The organisations that struggle are usually the ones that bought the interpretation and assumed the implementation would follow.
Not necessarily. Consent is the default, but Section 7 of the Act lists "certain legitimate uses" where you can process data without it, for example when a person has voluntarily given data for a specific purpose and hasn't objected. Leaning on consent for everything creates fatigue and brittle records. Leaning on exemptions without writing down why invites trouble.
The real work is deciding, purpose by purpose, which basis applies, recording the reasoning, and designing notices that match. It's one of the first things we settle in a baseline.
The Rules ask you to take due care that the person consenting is an identifiable adult, using reliable details you already hold or a virtual token such as one issued through DigiLocker. In a village that means designing the check into enrolment itself: an OTP to the guardian's number, a field worker's attestation, an ID reference recorded once.
Some education, health and child-care uses are exempt for specific purposes. Knowing exactly which of your programmes qualify saves a great deal of unnecessary friction.
For personal data processed on consent given before the Act commenced, you must give people a notice as soon as reasonably practicable, and they can withdraw. In practice that is a triage: delete what you can't justify keeping, and re-notify everyone else.
This is usually the largest single piece of work in a programme and the most neglected, because it lives in old registers and spreadsheets rather than in any one system.
The government notifies Significant Data Fiduciaries based on factors such as the volume and sensitivity of data processed and the risk to people's rights. If you are notified, you need a Data Protection Officer based in India, an independent data auditor, and periodic impact assessments and audits.
Large platforms, health and education networks and big employers should plan as if the label may arrive. Building the evidence trail now is far cheaper than reconstructing it later.
No. The Rules arrive in phases: the Data Protection Board from November 2025, Consent Manager registration from 13 November 2026, and most obligations from 13 May 2027. That last date is when obligations begin, not when the work ends. You will launch new programmes, sign new vendors and hire new staff every month. The real test is whether a programme you start next year collects data correctly without us in the room.
We measure our own success by that, and it's why change management sits inside the journey rather than after it.
Yes, and you shouldn't wait. Start by asking for a consultation session with us. We'll look at what you actually hold and pick the few things that matter most for an organisation your size.
Then deploy the Commons Trust software to look after your compliance needs day to day: notices, consent records, requests and evidence, without needing a dedicated privacy team.